Evidence recorded automatically
Policy decisions are recorded as they happen, and every change to your governance posture lands in an append-only audit log. Producing a report is an export, not a data-collection exercise across four teams.
Comply
Qastel turns what your AI estate actually did into audit reports for your DPO and executive summaries for your board, generated on demand or on a schedule.
Regulation keeps changing, and an auditor asks for history you can only show if it was recorded at the time. Qastel keeps that record and turns it into reports on your AI activity, so you stay on top of changing requirements and ready for an audit.
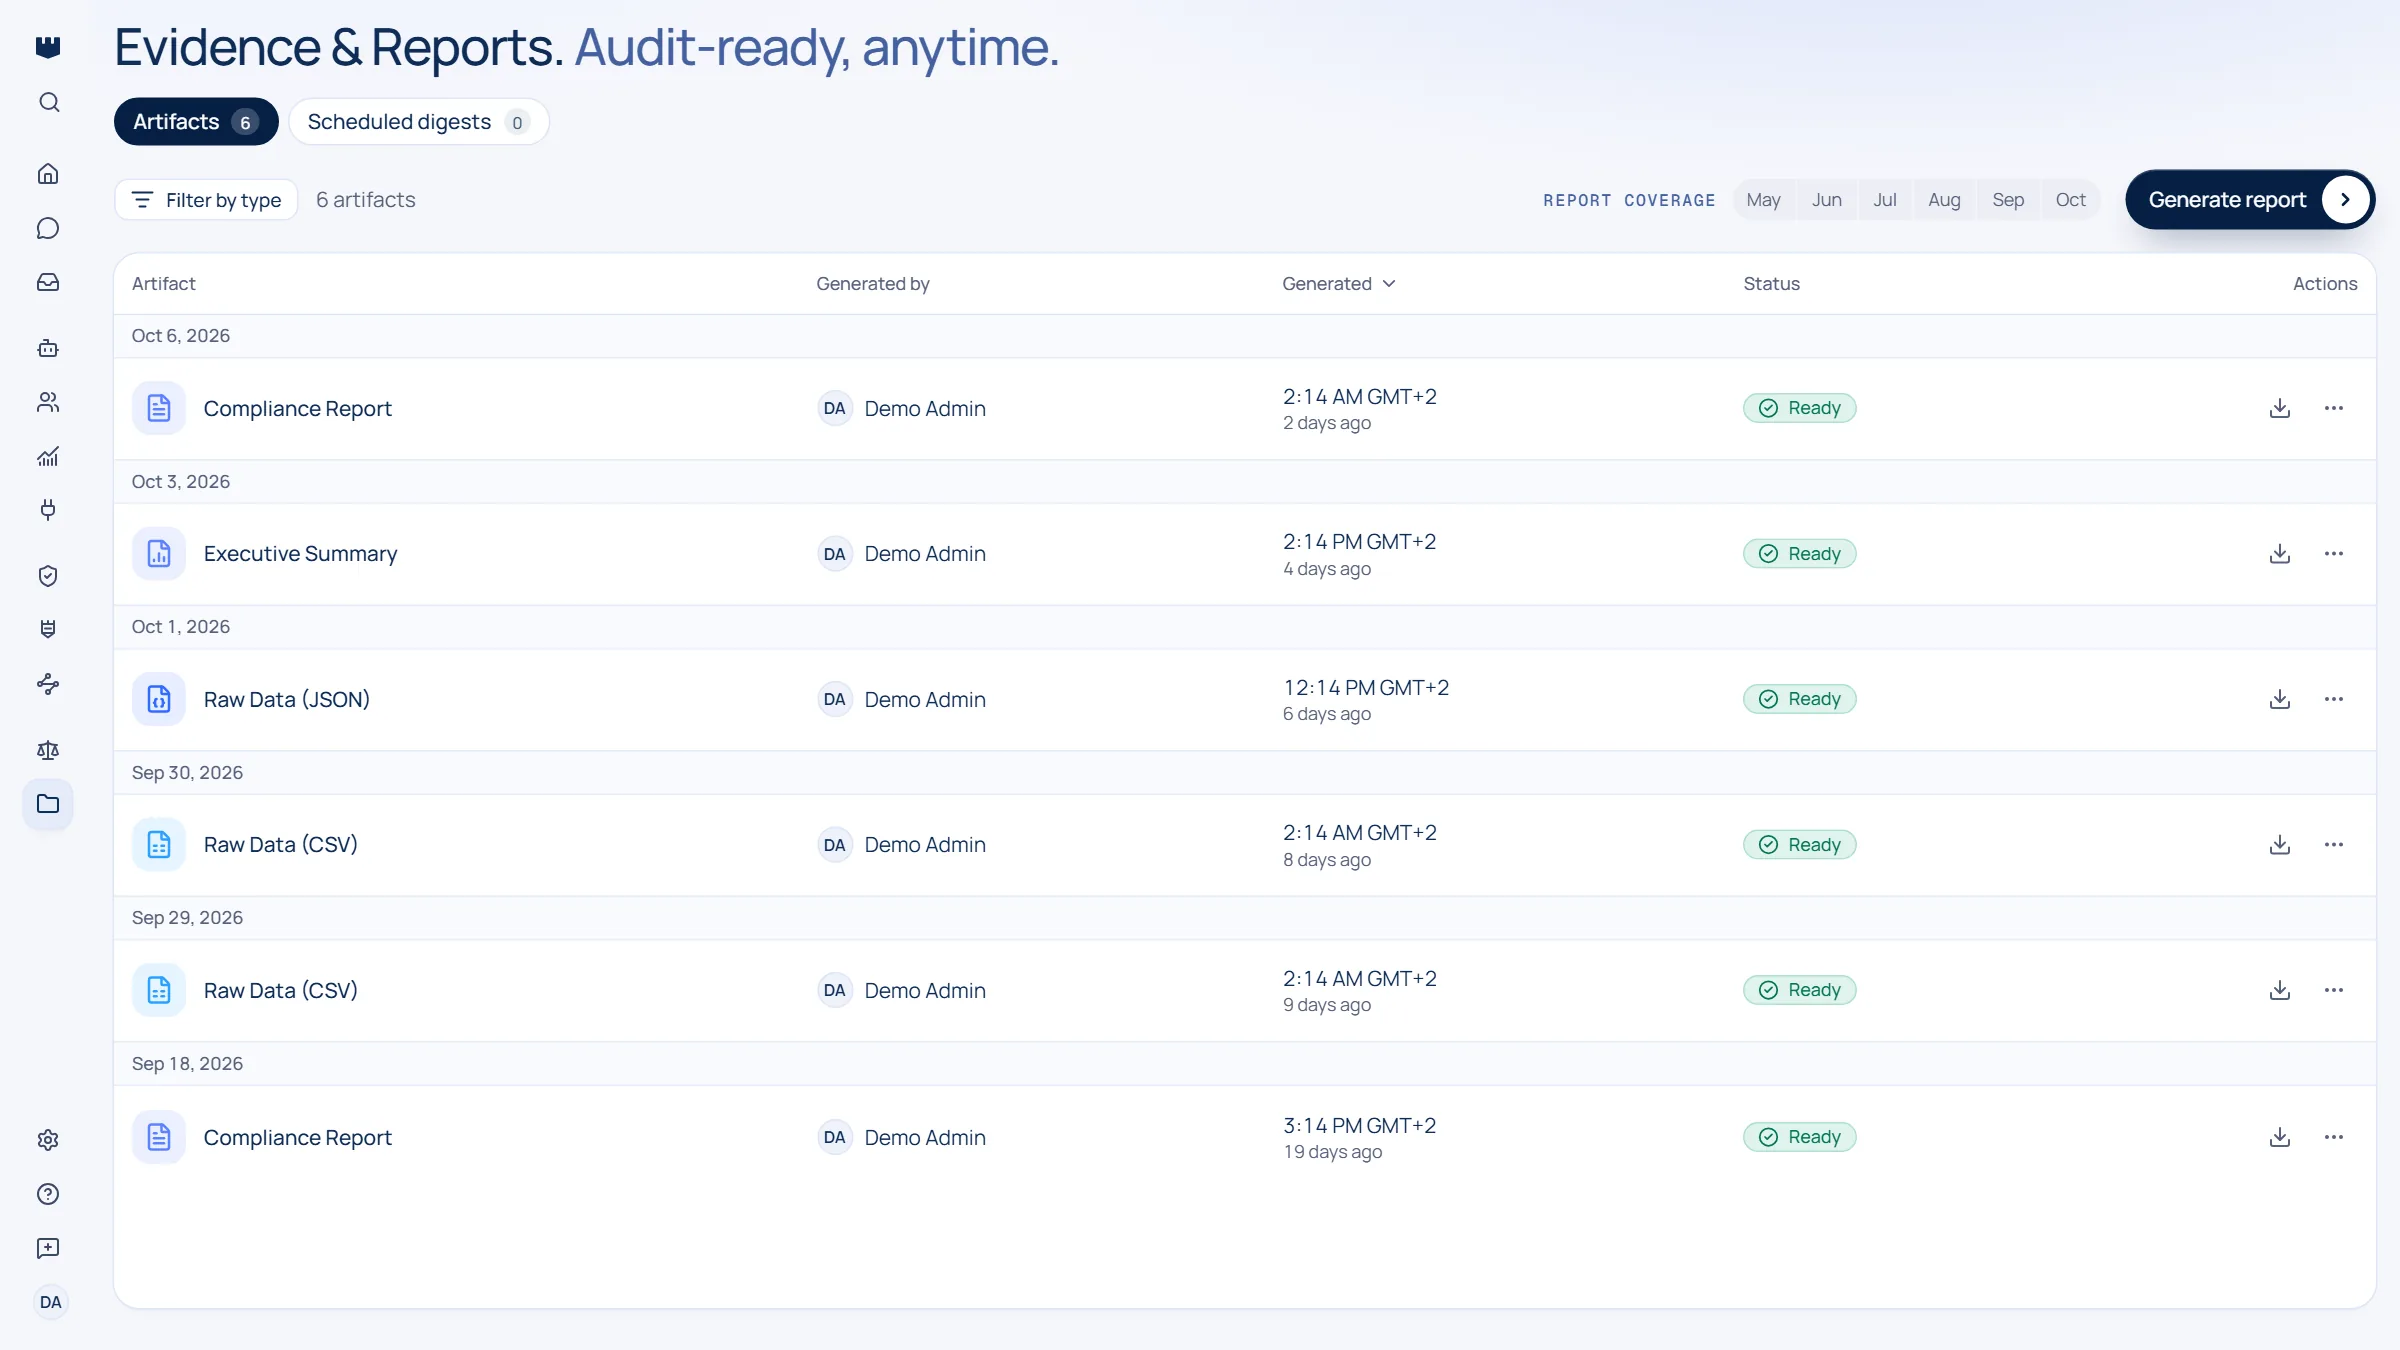
A Compliance Report with your EU AI Act evaluations, violations and recommendations, over 7, 30 or 90 days.
An Executive Summary of your risk posture, with charts, ready to share with leadership.
Scheduled digests email the reports to the people you choose, daily, weekly or monthly.
Audit reports
Generate a Compliance Report in a few clicks. Every report is kept on the Evidence and Reports page, so you can download it again months later when an auditor asks.
Board reporting
The Executive Summary gives leadership a high-level view of your AI risk posture. Attach it to a scheduled digest and it reaches your executive committee by email, with nobody assembling slides.
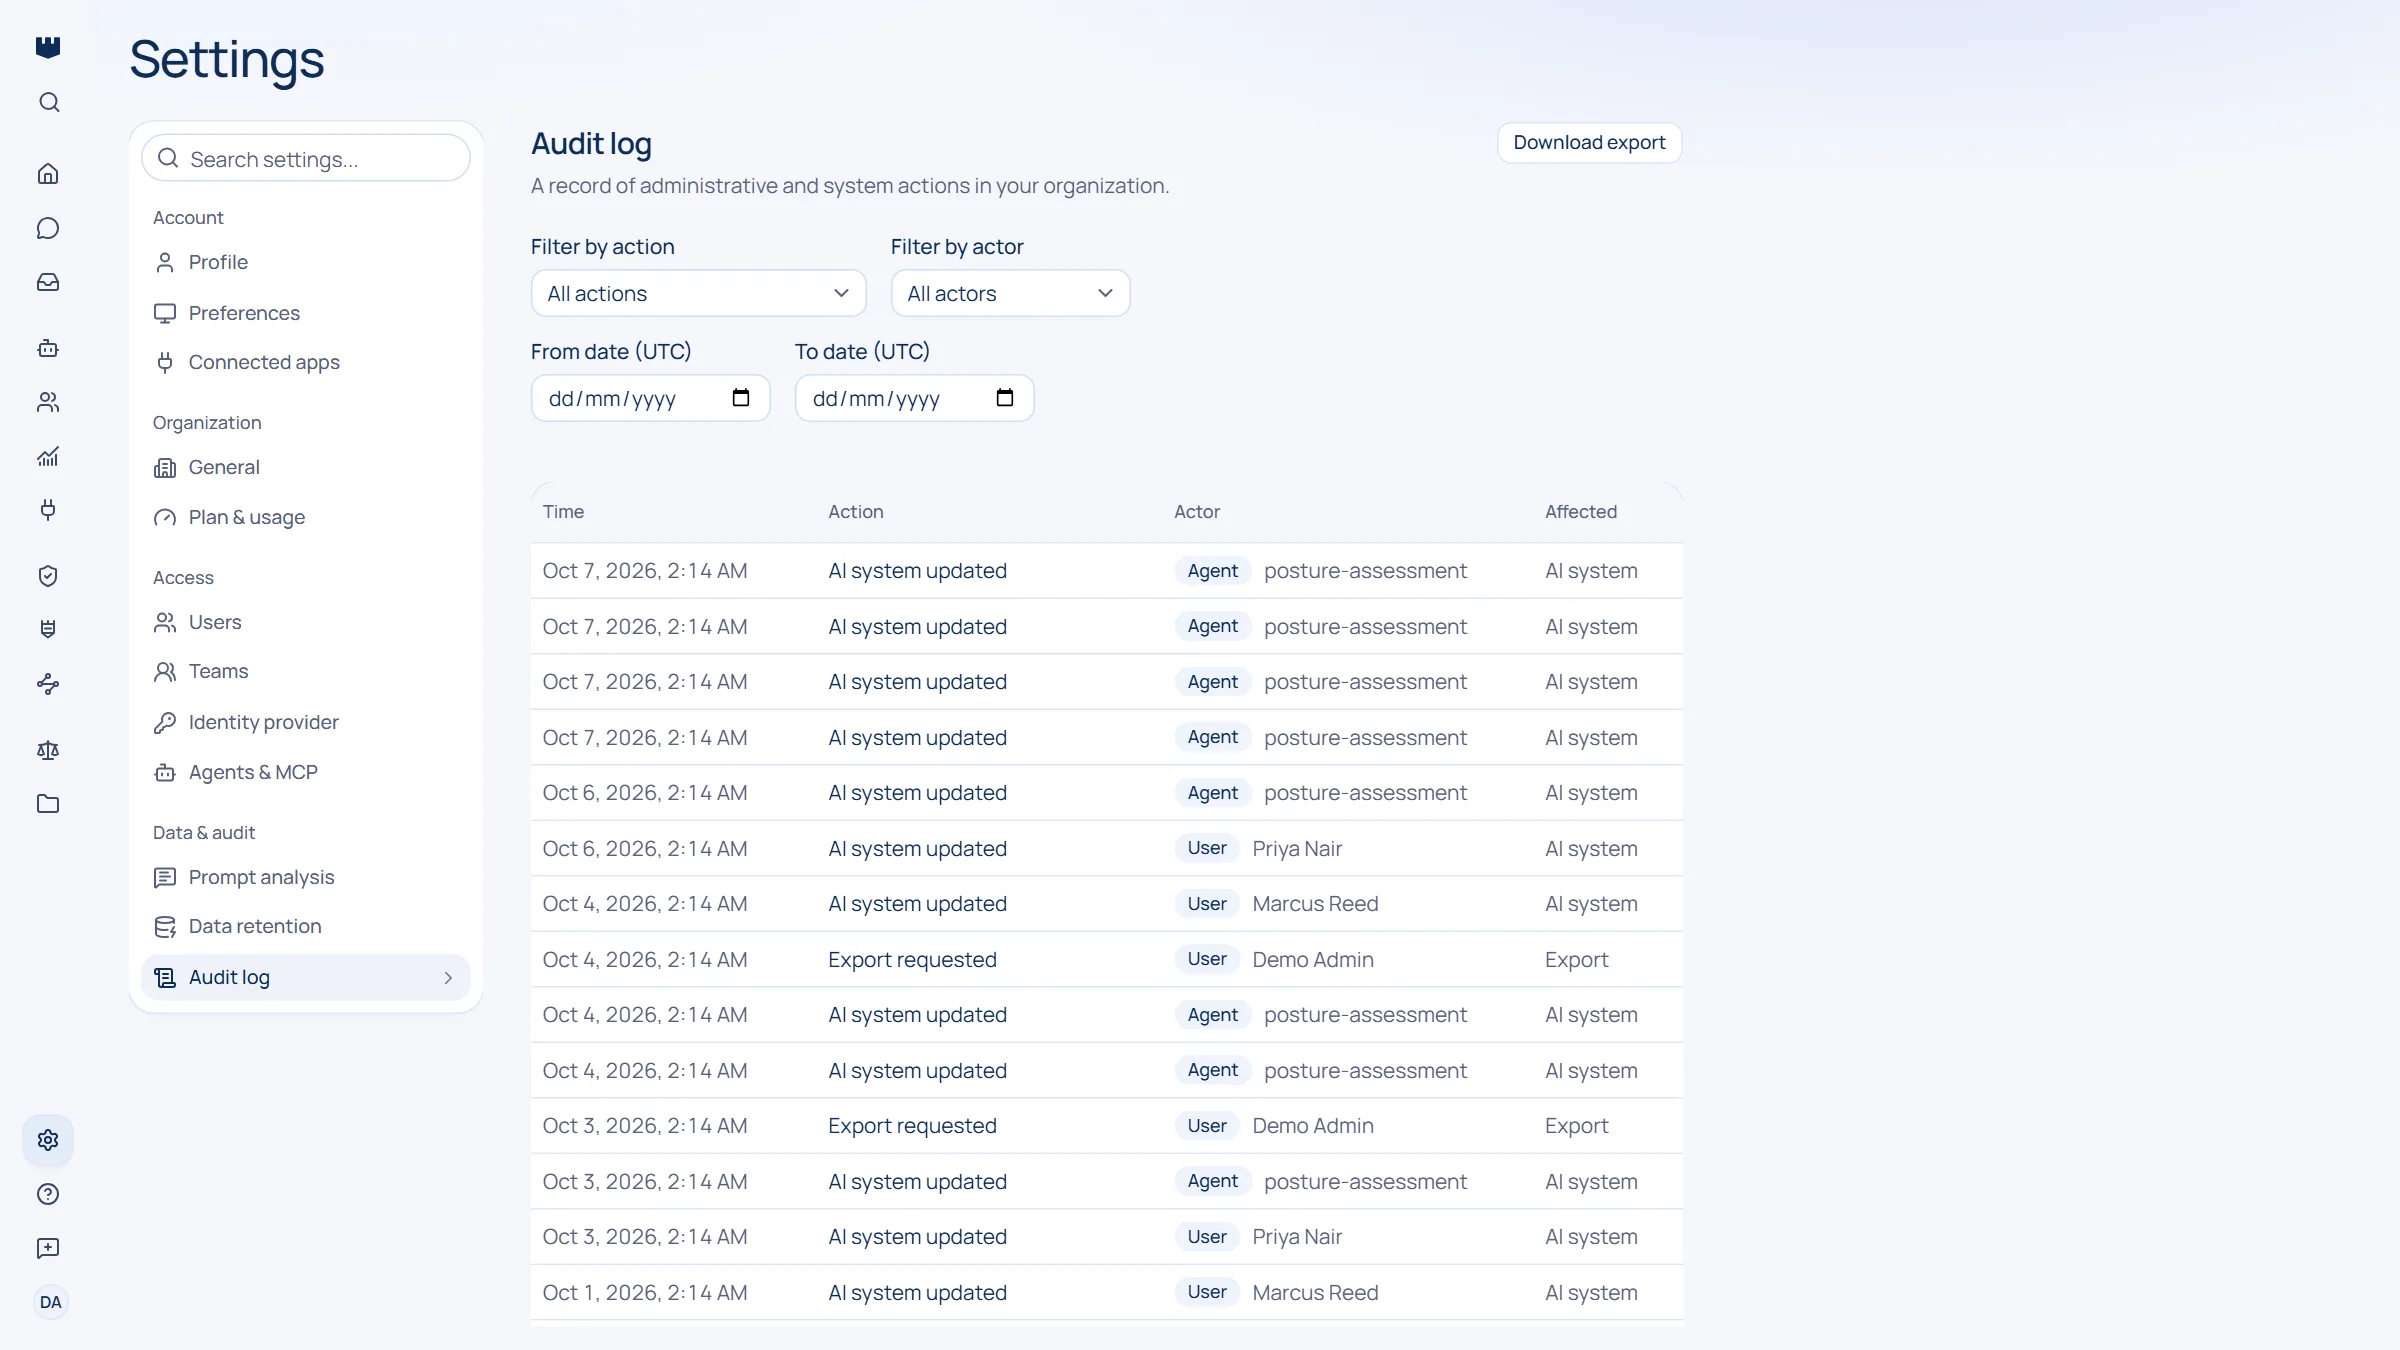
Audit log
Every change to your governance posture is written once and never rewritten: who changed a policy, a governance state or an owner, and when.
The Qastel difference
Policy decisions are recorded as they happen, and every change to your governance posture lands in an append-only audit log. Producing a report is an export, not a data-collection exercise across four teams.
Compliance state moves with the estate. A newly discovered high-risk system shows up as an open obligation the day it is found, instead of surfacing at the next annual review.
Europe sets the strictest rules on AI. Qastel is built and hosted here, and designed around those rules first, starting with the EU AI Act and GDPR.
Frameworks
Qastel classifies every AI system against the EU AI Act. For the other frameworks your auditors use, each policy carries the reference it serves, and its decisions are recorded as evidence under it.
Classified by Qastel
The risk tier and the obligations that follow attach from the day a system appears in the inventory.
Evidenced by your policies
A policy names its framework, reference and control, and every decision it makes is recorded against the exact revision that produced it.
Your own control catalog works the same way: an internal reference such as SEC-4.2 is carried exactly like a published one.
Outside the EU AI Act these are frameworks Qastel's policies can cite, not control mappings Qastel ships pre-built: you bring the mapping, and Qastel keeps the runtime evidence attached to it. Compliance with each of them remains your decision, and Qastel supplies the evidence for it.
For an organisation that uses AI rather than builds it, the Act means classifying each AI system by risk, stopping prohibited uses, making sure staff are AI-literate and, for high-risk systems, assigning human oversight, keeping logs and informing the people affected. None of that is possible without knowing which AI you run. Qastel keeps that register, classifies every system against the Act's risk tiers, and records policy decisions and governance changes, so the reports your DPO needs are generated from the record. How the Act applies to your organisation remains a decision for you and your legal counsel.
The Compliance Report covers your EU AI Act evaluations, violations and recommendations over the time range you pick: 7, 30 or 90 days. The Executive Summary gives a high-level view of your risk posture, and the raw data exports carry assets, policy evaluations and observations as CSV or JSON.
Yes. An admin creates a scheduled digest with a daily, weekly or monthly cadence, a list of up to 50 recipients and the reports to attach. Each file a schedule produces is also kept on the Evidence and Reports page.
No. The audit log is append-only: entries are written once and are never rewritten, so what the record showed at the time of an incident is what it shows at the audit.
Yes, with one distinction worth being precise about. Qastel classifies systems against the EU AI Act and only the EU AI Act. For every other framework, a policy carries the reference and control it exists to satisfy, and each decision that policy makes is recorded against the exact revision that produced it, so the evidence lands under your mapping rather than one we shipped.
Get a 30-minute overview of how Qastel discovers, assesses and controls the AI used across a business.